
Structures and Systems
Eisai’s Board of Directors has established the "Rules on the Development of Systems Necessary to Ensure the Proper Execution of Duties by Corporate Officers, etc.," which stipulate the establishment of a system for the retention and management of information, the establishment of necessary rules and procedures, and the responsibility to each Corporate Officer for managing risks of loss within their assigned duties.
In accordance with these Rules, the Corporate Officer responsible for personal information protection and confidential information security has established the information management structure, while the Chief Information Officer (CIO) is leading efforts to strengthen information security governance across the global organization.
The status of these initiatives is reported regularly to the Board of Directors and the Audit Committee.
External audits, certification acquisition, etc.
Our group, that handles important information including personal information, has obtained ISMS (Information Security Management System) certification and Privacy Mark accreditation.
As of FY2026, three companies within the Group in Japan, namely Arteryex Inc., Sunplanet Co., Ltd., and EcoNaviSta Inc., have obtained these certifications or accreditations.
-
1.
-
2.
-
3.
Policy and Basic Concept
The Company considers information security to be one of its important management issues (materiality). The Company regards the impact of cyberattacks and data leaks on its business activities, research and development, and on patients and people in the daily living domain as significant risks. Under the oversight of the Board of Directors, the Company is committed to risk assessment, protection of information assets, employee training, incident response, and continuous improvement.
Basic policy from the perspective of ensuring the security of confidential information
(Excerpt from the Eisai Network (ENW) Confidential Information Security Policy)
Based on the following basic policy, the Company has established and operates a system encompassing both business management (operational management) and system control.
-
(a)Properly identify and manage Confidential Information in the possession of each ENW company and to prevent any unauthorized access or disclosure thereof;
-
(b)Appropriately deploy and control IT systems to secure electronically stored Confidential Information and help improve business efficiency and productivity, and properly and efficiently utilize such IT systems in business activities;
-
(c)Develop and implement proper procedures for the proper acquisition, preparation, use, disclosure, storage and destruction of Confidential Information;
-
(d)Develop and implement proper procedures to ensure the security and confidentiality of Confidential Information by any Eisai Personnel, even after their resignation or retirement from the ENW companies, or otherwise end of their employment or assignment, unless otherwise restricted by applicable laws and regulations;
-
(e)Provide all Eisai Personnel with education and training on a regular basis related to maintaining the security and confidentiality of Confidential Information, thereby enhancing awareness about securing Confidential Information and ensure that any and all relevant procedures are complied with;
-
(f)Carry out company evaluations and audits, evaluate and, as appropriate, revise the information security structure and the operational status of the prescribed procedures on a regular basis, and ensure that improvements are made where appropriate;
-
(g)Comply with applicable laws and regulations pertaining to information security as stipulated in each country or region where Confidential Information is stored or where the organizations of ENW companies operate; and
-
(h)Develop and implement procedures to promptly investigate, respond to minimize the damage of, and take necessary measures to work to prevent recurrence of, security incidents (potential or actual).
Approach to Business Partners
The Company has established the “Eisai Global Code of Conduct for Business Partners” which applies to all Business Partners and their employees, including contractors, agents, suppliers, vendors and all other local and foreign entities acting on their behalf worldwide (“Business Partners”).
Within this Code, we stipulate requirements concerning data privacy and security, including compliance with applicable privacy and data protection laws and the protection, security, and lawful use of personal data.
Furthermore, in contracts concluded with business partners, we include clauses regarding confidentiality and the protection of personal information, clearly setting forth the mutual obligations of the parties regarding the handling of confidential and personal information and striving to ensure information security through mutual agreement.
For details about the “Eisai Global Code of Conduct for Business Partners”, please refer here.
Risk Management
While the use of IT and digital technology is advancing, cyber attacks are becoming more sophisticated and devious day by day, and ransomware, targeted email attacks, and attacks via supply chains, such as external contractors, are increasing the risk of shutdowns and other impacts on business activities. The Group holds many diverse and important information assets, including personal information, undisclosed information, and confidential information shared with partner companies. If this important information were to be leaked, tampered with, or lost, it could lead to legal liability, loss of competitive advantages, and even loss of corporate credibility. In particular, the Group is required to respond appropriately to personal information protection regulations globally, and leaks of unreleased structural formulas for projects in the drug discovery phase could directly affect the filing and acquisition of patents.
To address these risks, under the leadership of the corporate officer responsible for internal control and the Chief Information Officer, the Group is taking the following multi-layered information security measures and is working to continuously strengthen governance related to global information security and implement related measures.
- Strengthen security governance globally
- Thorough evaluation of the importance of information and access management
- Assess risks including system vulnerability and classify information, and strengthen the robustness of the system infrastructure foundation in accordance with data ratings
- Establish an immediate recovery framework to maintain the stable supply of pharmaceuticals and ensure business continuity
- Introduce functions that enable classification and protection according to the confidentiality level of information handled
- Prepare and periodically review rules related to confidential information management, including the Eisai Network Companies (ENW) Confidential Information Security Policy, rules related to personal information protection, and rules related to IT security
- Provide information security education and training for all corporate executives and employees (targeted email attack training, e-learning, etc.)
- Monitor information security threats, including cyber attacks
- Establish a response framework for incidents
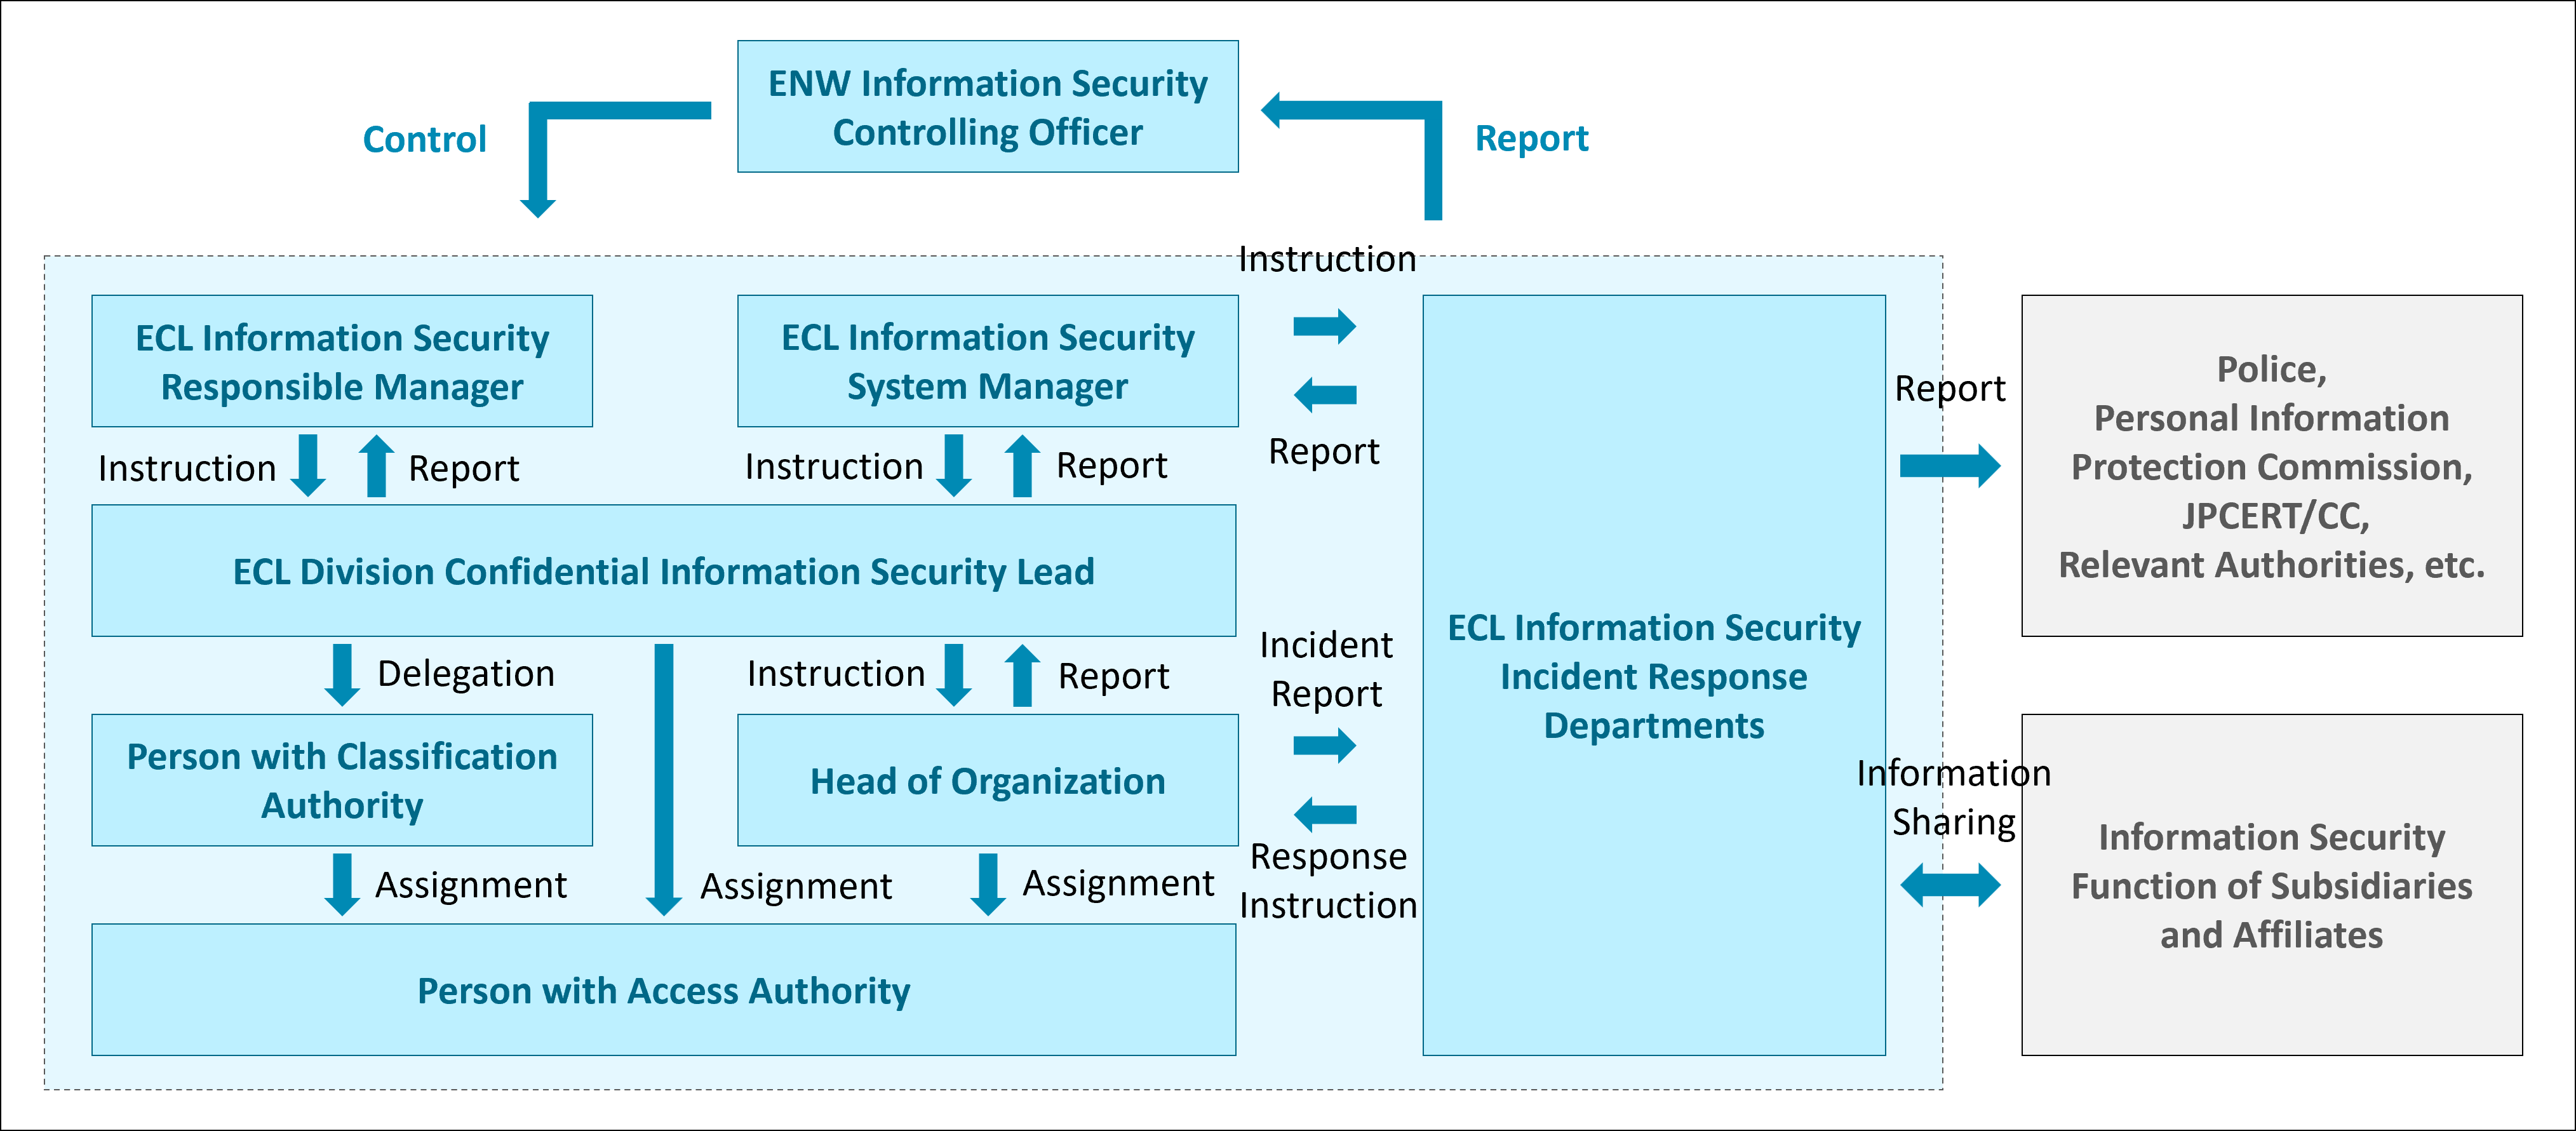
Information security incident reporting system
The Company defines an information security incident (hereinafter referred to as "incident") as any event that negatively impacts on the confidentiality, integrity or availability of Confidential Information or any ENW company’s IT system.
Such incidents are detected and reported both internally and externally by IT system administrators, departments handling confidential information, business partners, and others. The Company has established and operates a reporting system to ensure that these incidents are reported in a timely and appropriate manner to the ENW Information Security Controlling Officer (the corporate officer in charge of internal control who manages confidential information security) and the ENW Information Security System Manager (CIO), according to the level of information, so that appropriate decisions can be made.
Handling of Personal Information
Click here for Privacy Policy.